


Vulnerability Description: Root password hardcoded in TimePictra installation files - CWE-798
Software Version: 11.3
NIST: https://nvd.nist.gov/vuln/detail/cve-2026-8332
CVSS: 8.8
Severity: High
Credits: Dario Emilio Bertani, Andrea Sindoni, Antonio Carriero, Marco Manieri, Vito Pistillo, Davide Renna, Manuel Leone
A malicious user with a low privileged shell, by reading a configuration file can discover the root password and access the system with the maximum privileges.
Prerequisites: access to the local files.
Step-by-step instructions and PoC
The TimePictra software suite is installed under the /opt/Microchip/TimePictra path. One of the files stored under this path contains sensitive cleartext passwords. One of these credentials appears to be both the password for cinetix and root users. The configuration file is under a directory owned by tpadmin user, which does not appear to be a privileged user (i.e. is not part of sudoesrs), and could use this information to escalate his privileges.
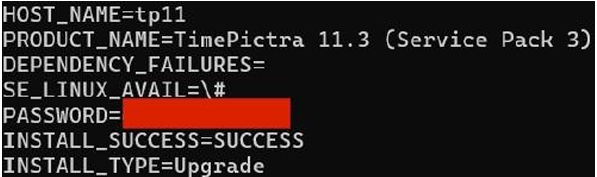
Figure 1
The file also contains base64 encoded credentials for the syncdb user, which seems to be related to the mysql DB running on ports 3306 and 33060, but any attempt to authenticate with the service with these credentials was not successful.
Security Impact
An attacker can retrieve the credentials and use them to gain unauthorized access, potentially compromising the entire system or related services.